True Native XDR.
Agentless.
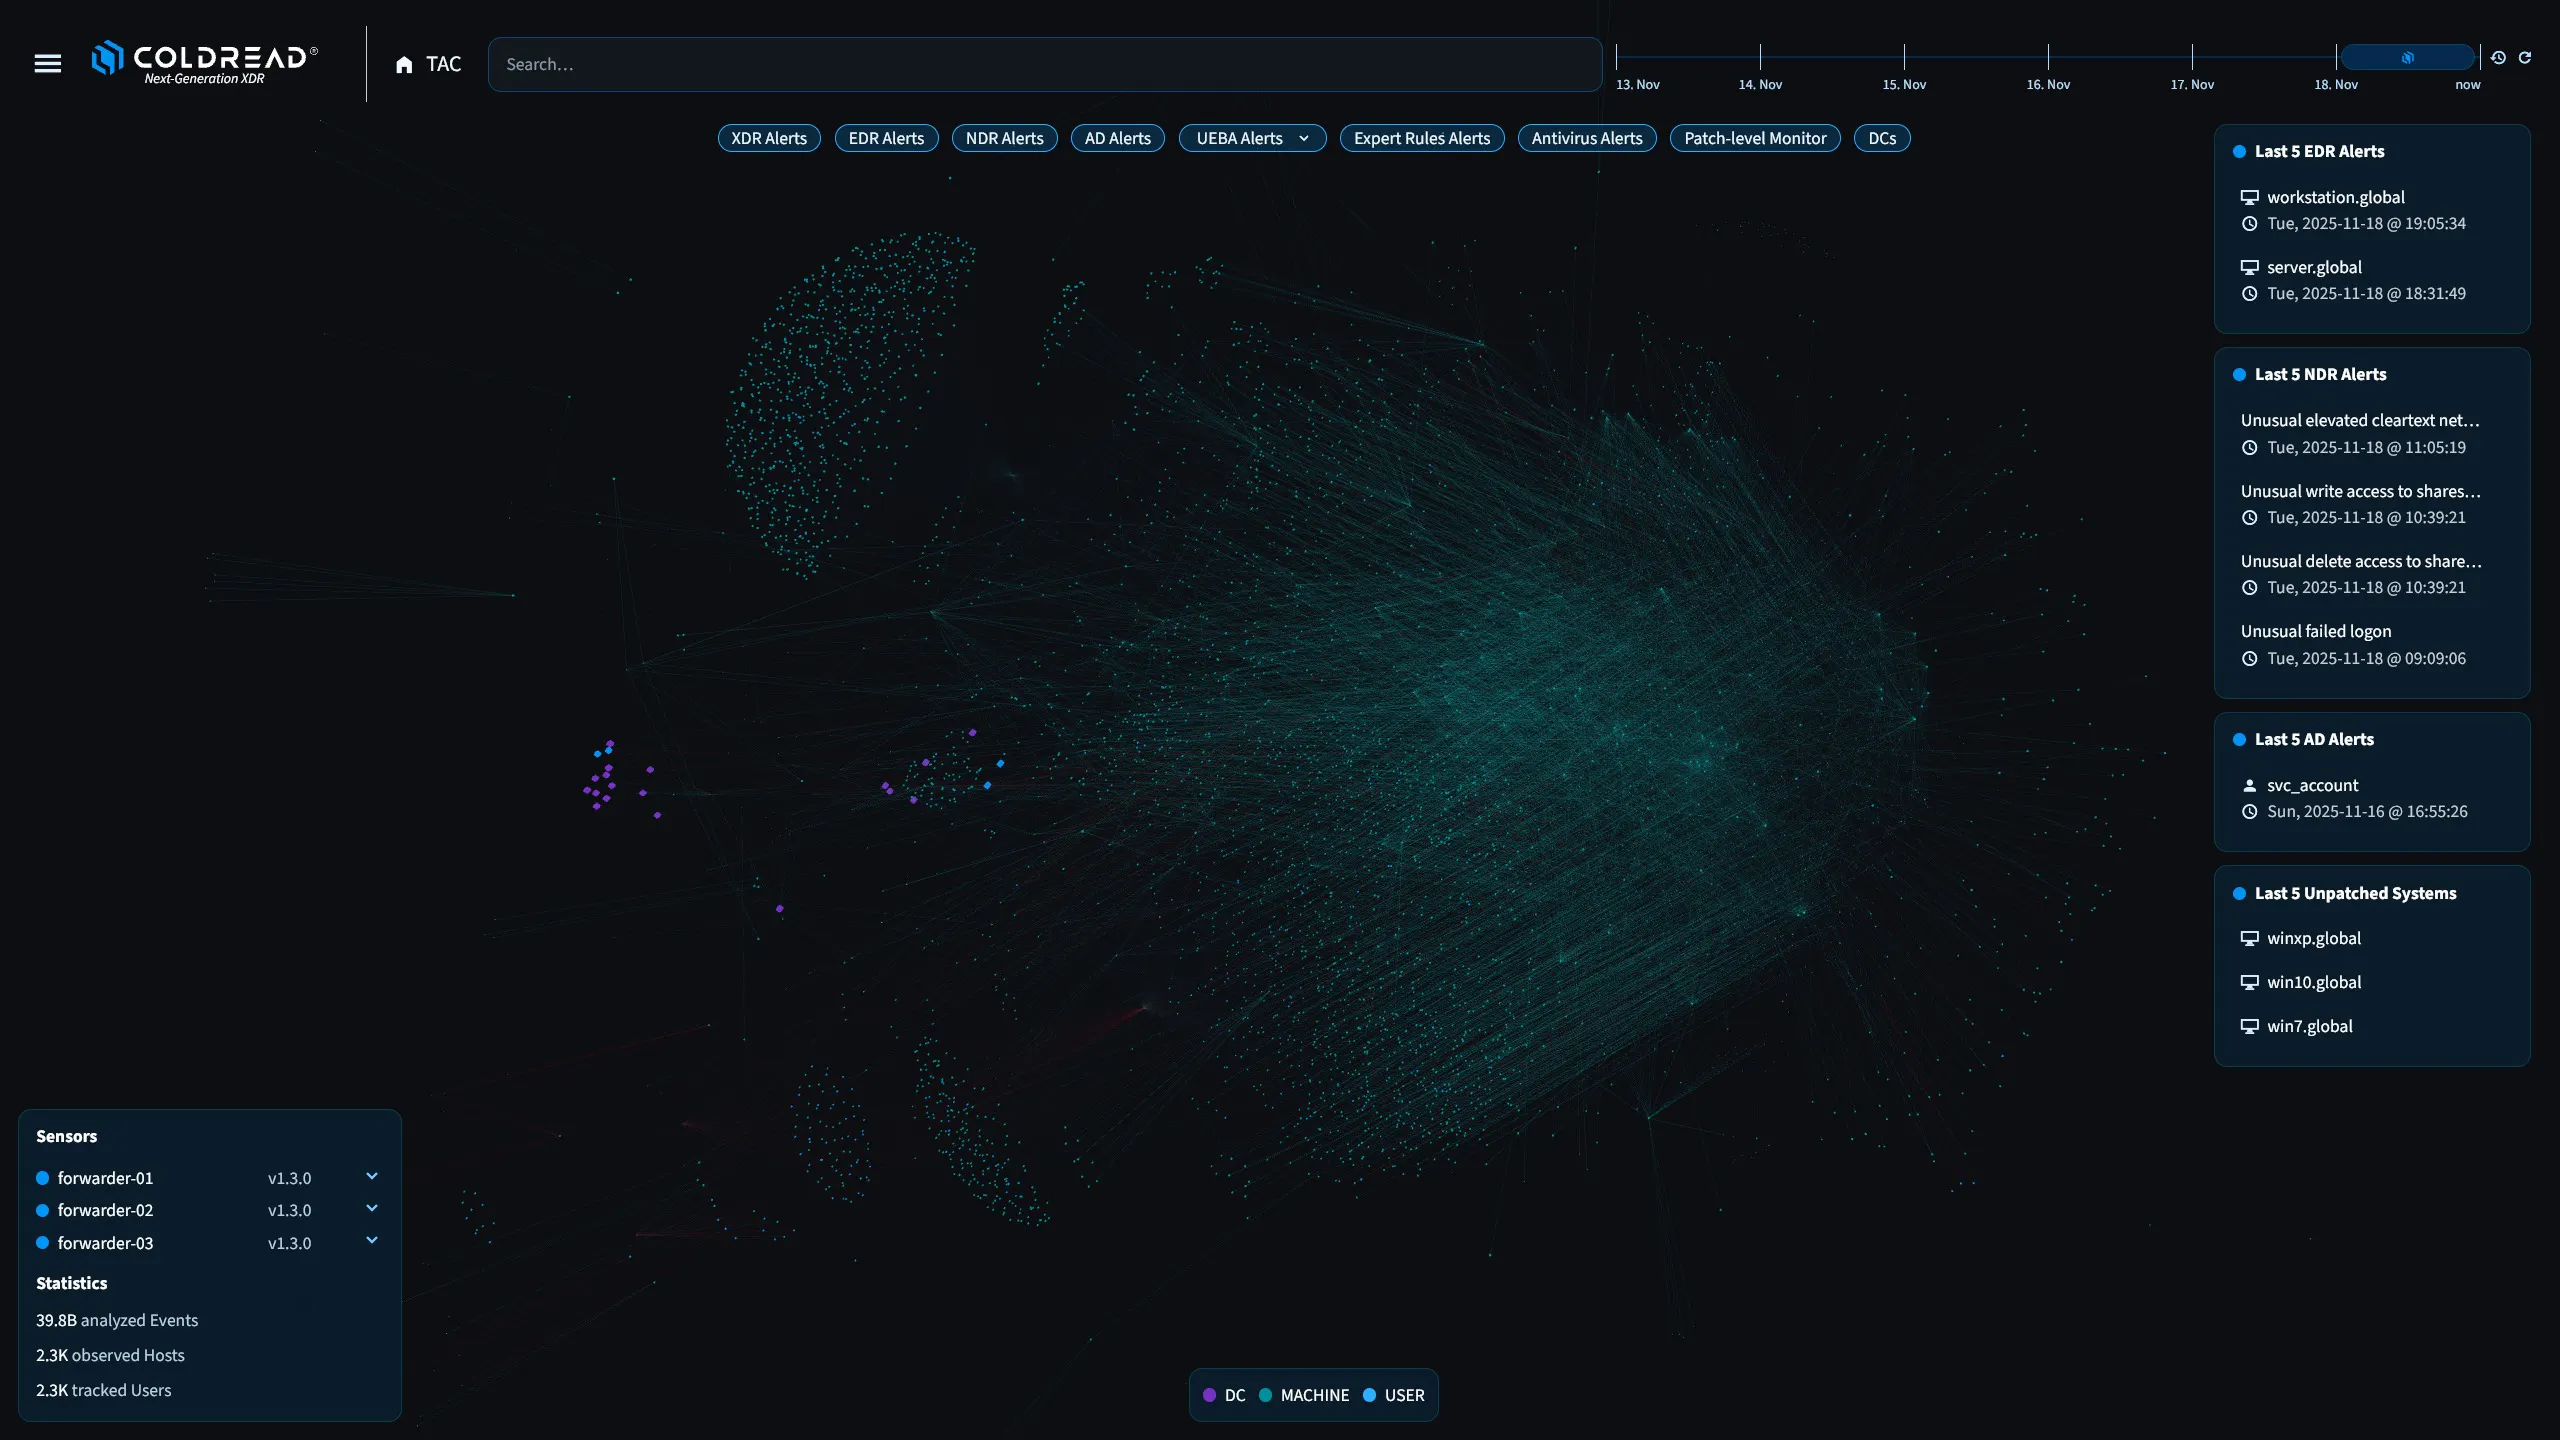
Coldread® learns how every user, device, and identity in your network behaves. Then it detects the attacks that rule-based tools miss. Live within hours.
Built on 12 years of red-team operations against DAX and ATX enterprises.
Enterprises and public institutions across DACH trust Coldread.
The platform
EDR, NDR, and SIEM. One platform.
One cloud-based threat detection platform, built entirely on native event logs. Every event is scored against learned behavior the moment it happens, not hours later in a batch job.
True Native XDR
Endpoint · Network · IdentityEndpoint visibility without an endpoint agent, network and entity analytics, identity monitoring, and UEBA. One sensor technology, one platform.
ML-SIEM
Behavior, not rulesBuilt as a machine-learning SIEM from the start. Anomaly detection across hundreds of thousands of behavioral models instead of a rule catalog.
Agentic SOC
Investigation at machine speedAnomaly detection surfaces the signal, agentic investigation builds the context, and our analysts validate before anything escalates.
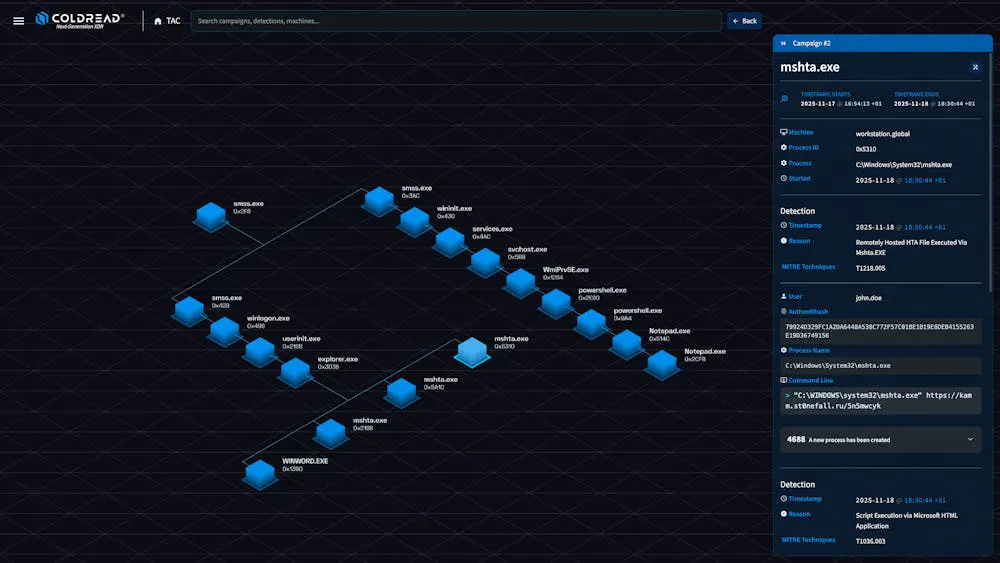
Endpoint protection. Redefined.
Our agentless EDR monitors endpoints without installing any software. It collects information directly from the host operating system and evaluates every process chain against the behavior it has learned for that device and user.
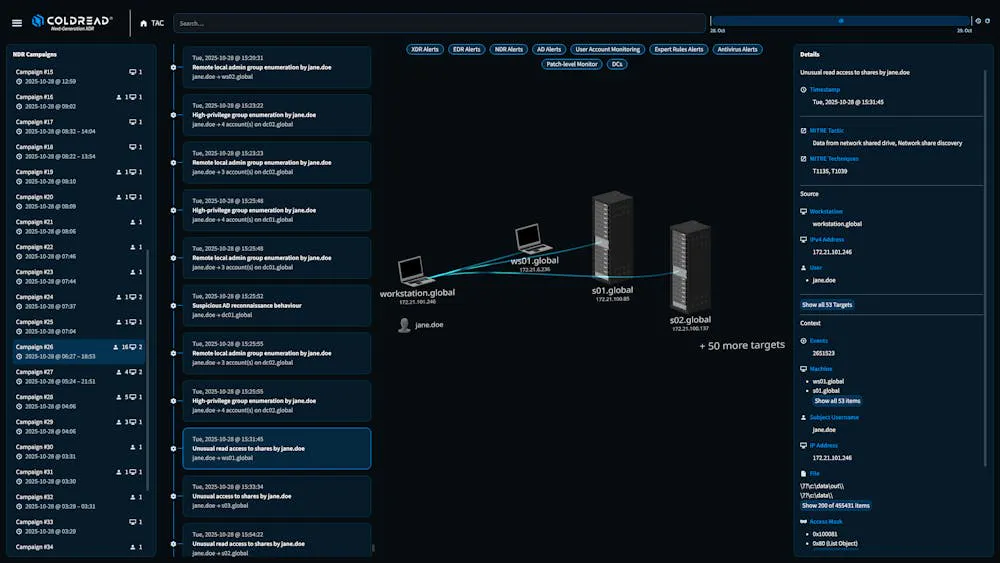
Network monitoring and Active Directory threat detection.
Coldread watches the entire internal network and every Active Directory identity, flags deviations from normal traffic, and warns early about advanced attacks such as brute force, lateral movement, and reconnaissance.
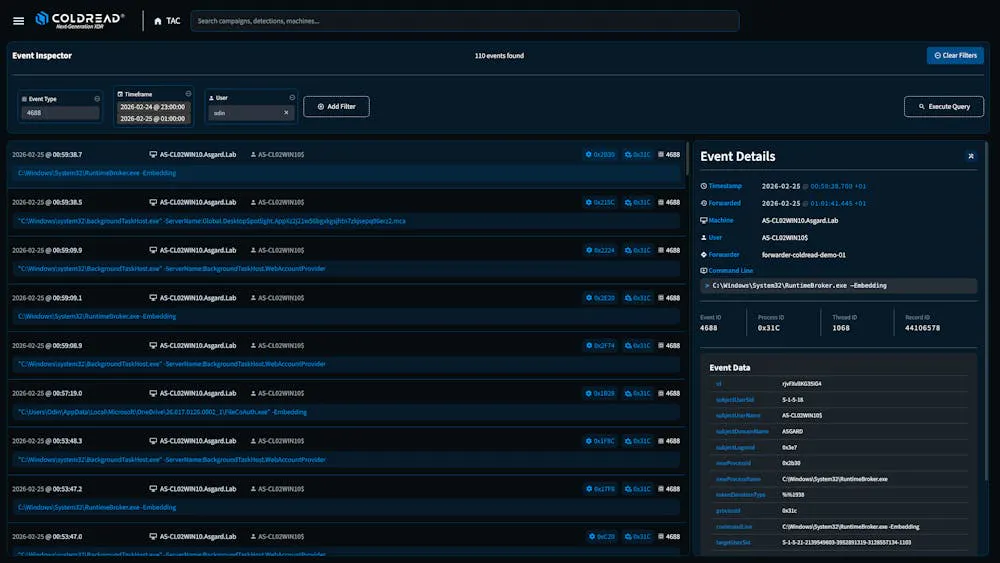
Every event. Stored, searchable, ready.
Every event forwarded to the Coldread® detection engine is mirrored into the data lake and stored for up to seven years. Specific timeframes can be extracted at any time, for insurance cases, incident response, or compliance audits.
See it live. In your network.
Thirty minutes with our team. We show you the platform on a live environment and how it would run in yours.
Coverage
One platform where others need three.
| Capability | Coldread® | EDR | NDR | SIEM |
|---|---|---|---|---|
| Agentless | ||||
| Agentic SOC | ||||
| Stealth | ||||
| Process anomaly | ||||
| Behavioral anomaly | ||||
| Network anomaly detection | ||||
| User Entity Behaviour Analytics | ||||
| Event log storage in data lake | ||||
| Host introspection | ||||
| AD monitoring & threat detection | ||||
| AD reconnaissance detection | ||||
| Privileged user monitoring | ||||
| Shadow IT discovery / patch level monitoring | ||||
| CIS / NIS2 / §8a regulatory conformity | ||||
| Managed SOC / MSSP | ||||
| Incident response |
Why Coldread
Security that respects your reality.
We protect mid-sized companies and large enterprises with prevention, detection, and remediation. Fully managed, machine-learning powered, one package with predictable costs.
Deployed in hours, not months
Rolled out across the network via GPO or Intune, without touching individual endpoints. No rollout project, no agent conflicts.
Invisible to attackers
Only telemetry is collected. Attackers find no running process to detect, manipulate, or switch off.
Detection that never sleeps
Anomaly detection and automated response run around the clock. Our threat hunters investigate what the system surfaces: thousands of automated hunts every day, validated by experts.
Incident response
In the event of an attack, our specialists isolate the affected endpoints immediately, prevent further spread, and eliminate the root cause.
Beyond the platform
Twelve years of offense, at your service.
The team behind Coldread spent over a decade breaking into networks like yours, legally. That experience is available as a service.
Red teaming
We simulate the tactics of advanced attackers under real-world conditions to test your systems and processes for weaknesses. The result is a security architecture that is more robust and resilient against real attacks.
Breach assessment
We assume an attacker is already inside your systems. We analyze how far they could spread, which data is at risk, and which gaps could be exploited. You get clear insight into your actual exposure.
AD security assessment
Our specialists review your Active Directory environment for misconfigurations, vulnerabilities, and potential attack paths. The result is a hardened AD infrastructure that reliably protects your identities.
Security consulting
We develop customized security strategies together with you and support you through implementation, so your business stays protected against current and future threats.
Run your SOC on Coldread.
Accelerate your Security Operations Center and raise productivity. Serve more customers with the same team: Coldread replaces the manual processes that overload your analysts.
Signals under analysis across our customer environments.
From manufacturing and logistics to public administration.
Mean time to identify and contain an attack, across Coldread customers.
Financial damage from breaches since Coldread's first deployment in 2020.
Industry figures: IBM Cost of a Data Breach Report 2025 · Coldread figures: customer base 2020–2025
Compliance
Audit-ready by design.
Up to 7 years of event log storage. The evidence your auditors, insurers, and regulators ask for is already there.
About Coldread
Simplified security. Amplified protection.
As cybersecurity experts, red teamers, and pen-testers, we kept running into the same problems: EDR solutions that attackers could bypass, complex rollouts that overloaded IT teams, and fragmented tools that left gaps.
With Coldread®, we built a platform that unifies EDR, NDR, and SIEM functionality in a single system. Today, Coldread® protects enterprises and public institutions alike.
Contact
Let's talk.
Would you like to learn more about how Coldread® and our fully managed service can protect your business? We usually reply within one business day.
Coldread® is a product of
Secattack GmbH
Kinkstrasse 40/3
A-9020 Klagenfurt